
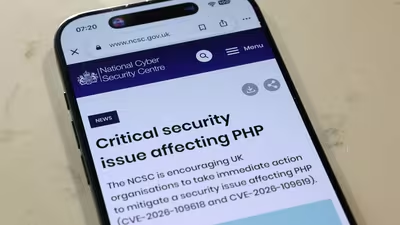
A flaw discovered by artificial intelligence in the PHP programming language has triggered a wave of shutdowns of various websites and government servers across the world.
This issue can result in the PHP leaving partially initialised internal data behind and later treating it as valid, corrupting memory. As per the non-profit group, a fatal error at the wrong point in the PHP could leave internal state pointing to memory that belonged to a previous request. The PHP language powers around 70 percent of the websites in the world, according to Alphabet-owned security firm Wiz. Vulnerability 1 – CVE-2026-109618: As per the PHP foundation, CVE-2026-109618, or Remote Code Execution (RCE) via OOM corruption, is among the two critical remote code executive vulnerabilities found. Vulnerability 2 – CVE-2026-109619: The other error is CVE-2026-109619 or RCE via stale global state. Both of these vulnerabilities have a score of 9.2 on the Common Vulnerability Scoring System (CVSS).
“Given the severity of these flaws and PHP’s widespread use, we consider this one of the most impactful security issues in recent memory,” said OpenAI in a statement.
